How to Protect the Machines You Run and Secure the Ones You Build
Most production machines were engineered to run reliably, not to defend themselves.
A packaging line or CNC cell built a decade ago typically sits on a flat network, still runs with default credentials, and uses controllers that trust any device that talks to them. That was acceptable while machines stayed isolated. Once they are linked to MES, remote service tools, and plant-wide analytics, every connected machine becomes a possible entry point, and the controller behind it rarely has a way to push back.
The pressure is not only technical. Plant operators need connectivity and visibility without exposing production. Machine builders face customers who now write security requirements into purchase specifications, and export markets such as the EU are adding cybersecurity obligations for machinery and connected products through the Machinery Regulation and the Cyber Resilience Act.
There is no single fix, because the right approach depends on where a machine is in its life. Equipment already in service needs protection placed around it, with no change to how it operates. A machine still in design can have protection chosen into each networked component. This guide covers both paths with Moxa hardware available through ManuAuto and shows exactly where each device sits inside a real machine.
 For installed machines
Need to Lock Down Machines Fast?
Looking to protect machines already running on the plant floor? Roll out security upgrades without changing PLC configurations or stopping production.
 For new machine builds
Designing a New Machine From Scratch?
Building a new machine? Specify secure-by-design devices so security is part of your architecture from the very first drawing.
LEGACY MACHINE PROTECTION
Secure Legacy Machines Without Touching PLC Code
The PLC is the core of every machine, so adding security should never get in its way. Zero-configuration protection shields your legacy assets without disrupting the network or requiring PLC reprogramming.
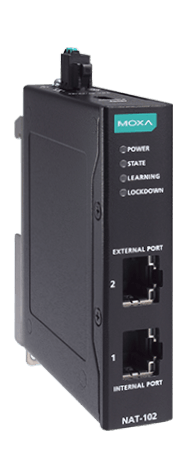
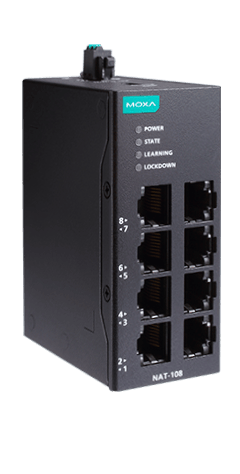
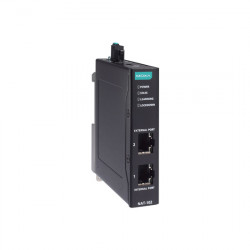
NAT-102 Series
2-port industrial Network Address Translation (NAT) devices
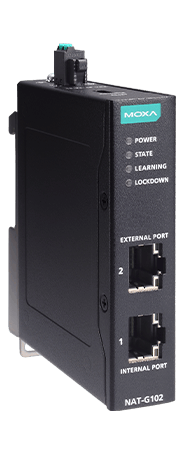
NAT-G102 Series
2-port industrial Network Address Translation (NAT) devices with 1GbE ports
NAT-108 Series
8-port industrial Network Address Translation (NAT) devices
Industrial NAT Devices
NAT-(G)102 / NAT-108 Series
NAT-(G)102 and NAT-108 devices use 1:1 NAT mapping to remove IP address conflicts, so rollouts across the plant stay smooth and predictable.

Easier IP Management

Hands-Free Network Access Control

Ultra-Compact Design
Industrial LAN Firewalls
EDF-G1002-BP Series
EDF-G1002-BP Series firewalls help OEMs build cyber-resilient equipment, keeping integration simple while production stays online.

Transparent Filtering Mode

Industrial DPI Technology

IPS and DoS Protection
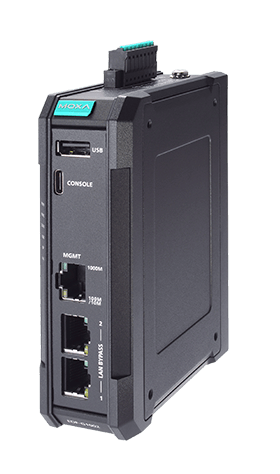
EDF-G1002-BP Series
Next-gen industrial LAN firewalls with 2 Gigabit ports
SECURE-BY-DESIGN COMPLIANCE FOR NEW MACHINES
Build Cyber-resilient Machines With Security Built In
Introduce component-level protection during cabinet design to eliminate security blind spots, streamline audits, and support regulatory compliance.
Secure by Design From the Start
Moxa products are developed under an IEC 62443-4-1 ML3 certified process, delivering secure hardware and software that integrate smoothly from day one.
Faster Supply Chain Approval
Get approvals faster with full SBOM management, security guides, and direct access to the Product Security Incident Response Team (PSIRT).
Stronger Day-to-Day Machine Defense
Role-based access control (RBAC), network access control, and event logs help you manage and protect machines throughout daily operation.
Long Life-cycle Commitment
Moxa's Product Life-cycle Management Policy keeps components available and security patches supported for the long term, so you avoid redesigning machines.
SOLUTION PORTFOLIO
Secure-by-design Edge Connectivity Solutions
NPort 6000-G2 Series
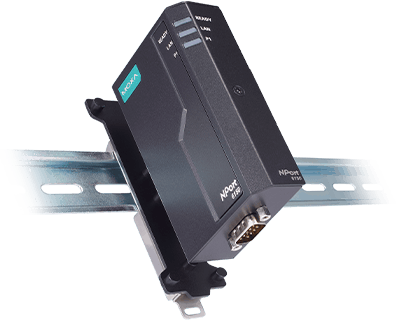
Secure serial device servers built around strong access control.
- Certified to IEC 62443-4-2 Security Level 2
- Centralized authentication and remote syslog for simple IT integration
- RBAC, syslog event logging, and protection for both serial data and management interfaces
MGate MB3170-G2/MB3270-G2/MB3470-G2 Series
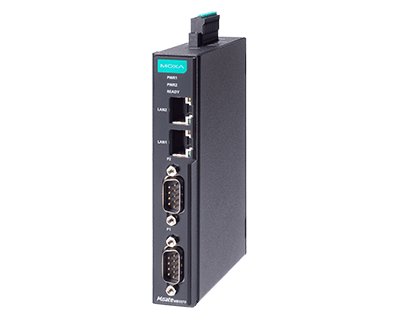
Advanced Modbus gateways featuring high-performance agent mode and hardened security.
- Meets IEC 62443-4-2 Security Level 2 requirements
- Comprehensive traffic logging and auditing
- Secure hardware boot loader protects against firmware-level threats
ioLogik 1400 Series
*Preliminary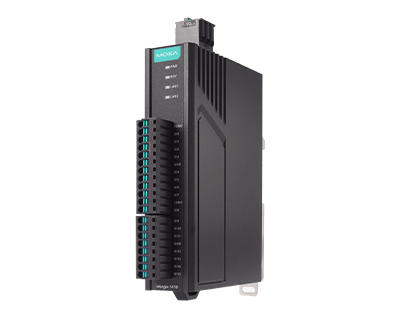
New-generation standalone Ethernet remote I/O with security built in.
- Meets IEC 62443-4-2 Security Level 2 requirements
- RSTP support for resilient Ethernet networks
- Push-in terminal blocks speed up wiring
*Expected availability: December 2026.
SDS-(G)3000 Series
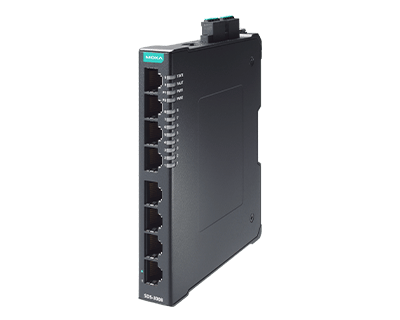
Ultra-compact smart switches for machine protection and easy PLC integration.
- Trusted access control protects the integrity of the machine network
- EtherNet/IP, PROFINET, and Modbus TCP support for seamless PLC integration
- Ultra-compact size fits tight control panels
Machine Security in Action: Real Industrial Scenarios
Adding Machine Boundary Security Without Reconfiguring PLCs
Building Secure-by-design Networks for Wind Turbine Systems
Most plants will not fit neatly into one path. A typical site runs older machines that must stay untouched alongside new lines still being specified, and the strongest results come from treating them as one plan: contain what is already running, and set a clear security baseline for everything that comes next. Starting with the machines that are most connected, or most critical to output, keeps the effort focused where exposure is highest. Before reaching out, it helps to have a short list ready: how many machines are involved, how they connect to the plant network today, which industrial protocols they use, and whether a customer or export market has set specific security requirements. With that in hand, ManuAuto’s team can recommend the right combination of devices for each machine and help you move from assessment to installation without guesswork.
Related Products